How the CRA Annex I checklist works
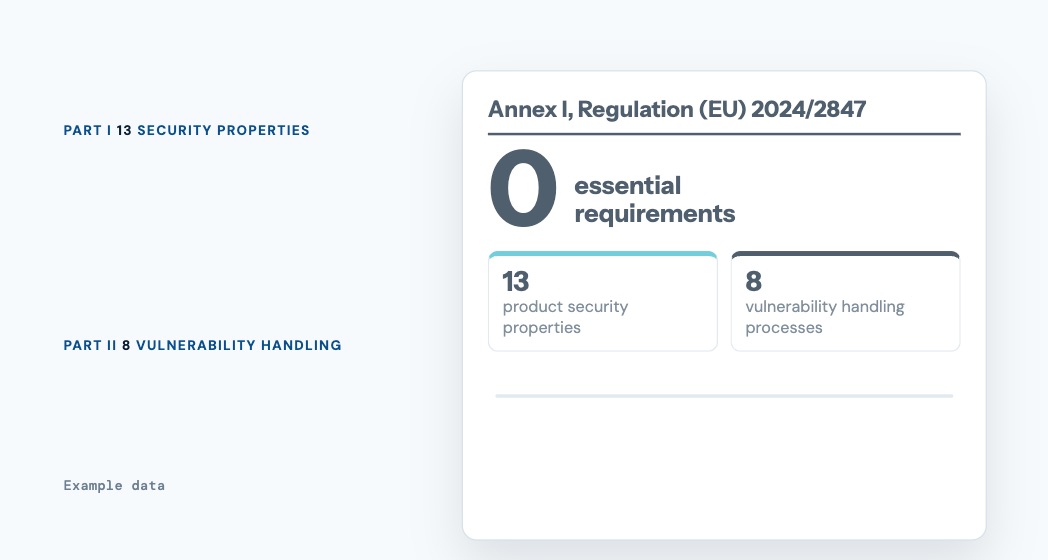
A 32-second loop: the 21 essential requirements in Annex I of the EU Cyber Resilience Act, scored for one instrument software product, with every gap given an owner and a date. Example data only.
CRA Annex I Checklist for Instrument Software
All 21 essential requirements as practical checks for lab instruments and their software. Free PDF, 10 printable A4 pages.
Download the free checklistFound gaps you can't close in-house? Book a free CRA readiness audit.
1 / 6 · The requirements
Annex I sets 21 essential requirements for your instrument software.
13 product security properties and 8 vulnerability handling processes, in full from 11 December 2027.
The requirements
Annex I of the EU Cyber Resilience Act sets 21 essential requirements: 13 product security properties and 8 vulnerability handling processes. Reporting has applied since 11 September 2026, and the full requirements apply from 11 December 2027.
One product
Complete one checklist per product, starting with your highest-volume instrument in the EU.
Part I
Score each product security property as Met, Partly, Not met or N/A, using practical checks for instrument software and the evidence to keep.
Part II
Score the 8 vulnerability handling processes. They apply to every product for its whole support period, and legacy software often has no SBOM.
Gap tracker
Give every gap an owner and a target date, then decide which products need work first.
Next step
Download the free checklist. If you find gaps you can't close in-house, book a free CRA readiness audit.
The checklist is guidance to support a self-review. It is not legal advice and completing it does not demonstrate conformity.
Download the free checklist