21 CFR part 11 Compliance Guide
What is 21 CFR Part 11 Compliance?
21 CFR Part 11 compliance is an FDA regulation that establishes the criteria under which electronic records and electronic signatures are considered trustworthy, reliable, and equivalent to paper records. It requires strict controls for data integrity, audit trails, and system validation in pharmaceutical and biotech environments.
Who has to comply with 21 CFR Part 11?
Part 11 applies to any FDA-regulated organization that keeps records required by another FDA regulation (a “predicate rule”) in electronic form, or submits them to FDA electronically. In practice that covers pharmaceutical and biotech manufacturers working under GMP (21 CFR 210 and 211), labs working under GLP (21 CFR 58), clinical research organizations and medical device makers. If an instrument, analysis program or spreadsheet produces a record you rely on for a GMP or GLP decision, that system is in scope.
What 21 CFR Part 11 requires
The regulation took effect on August 20, 1997 and has three subparts:
- Subpart A, General provisions (11.1 to 11.3): scope, implementation and definitions, including the difference between closed and open systems.
- Subpart B, Electronic records (11.10 to 11.70): the controls a system must have, how signatures appear on records and how each signature is linked to its record.
- Subpart C, Electronic signatures (11.100 to 11.300): who may use an electronic signature, how it is built from an ID and password or a biometric, and how those credentials are controlled.
Section 11.10 lists the controls most inspections focus on. For a closed system you need:
- Validation of the system for accuracy, reliability and consistent performance
- Accurate and complete copies of records in human-readable and electronic form
- Protection of records so they can be retrieved throughout the retention period
- Access limited to authorized individuals
- Secure, computer-generated, time-stamped audit trails that record who created, changed or deleted a record, without obscuring the original entry
- Operational, authority and device checks
- Training for the people who develop, maintain and use the system
- Written policies that hold individuals accountable for actions taken under their electronic signatures
- Controls over system documentation
How FDA enforces Part 11 today
In its 2003 guidance, Part 11, Electronic Records; Electronic Signatures: Scope and Application, FDA narrowed how it interprets Part 11 and said it would use enforcement discretion for validation, audit trails, record retention and record copying, while still enforcing the underlying predicate rules. That does not make those controls optional. Data integrity findings still appear regularly in FDA warning letters, and inspectors expect audit trails, unique logins and validated systems for any GMP record.
How to become 21 CFR Part 11 compliant in five steps
- List your GxP systems. Identify every instrument, analysis package and spreadsheet that creates or stores a record required by a predicate rule.
- Assess each one against section 11.10. Use our 21 CFR Part 11 compliance checklist to find the gaps in audit trails, access control and signatures.
- Close the gaps in the software. Upgrade, replace or wrap systems that cannot keep an audit trail or apply electronic signatures. AuditSafe 21 CFR Part 11 compliance software adds these controls to the software you already run, without a rebuild.
- Validate. Document installation and operational qualification (IQ/OQ) and keep the evidence ready for inspection.
- Put the procedures in place. Write SOPs, train users and certify your electronic signatures to FDA before you rely on them.
How AuditSafe Ensures 21 CFR Part 11, ALCOA and EU Annex 11 Compliance
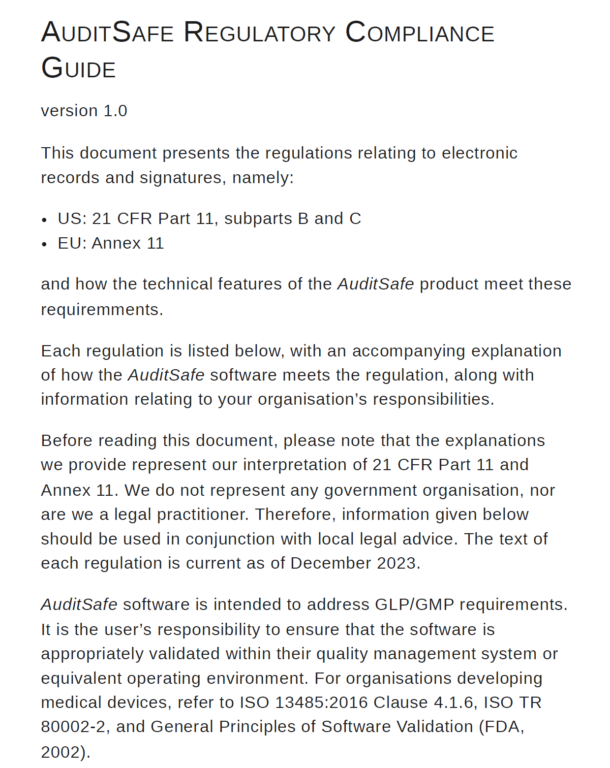
This document presents the technical features of our AuditSafe software and how it complies with respect to FDA 21 CFR part 11 subpart B – Electronic Records and EU Annex 11 and how these individual regulations can be satisfied to help your organization comply with them.
Each regulation is translated in easy to understand terms and explained to present a more easy-to-read document.
We outline how our AuditSafe software and the customer’s organization share the responsibilities for compliance and where the boundaries for each lie.
Before reading the document please note that the explanations we provide represent our interpretations of the 21 CFR part 11 regulations. We do not represent any government agency.
The regulations we provide are true to the publishing date.
AuditSafe is intended to facilitate FDA 21 CFR Part 11, EU Annex 11, ALCOA, GAMP5 and more general GMP/GxP compliance. It is the user’s responsibility to ensure that the software is appropriately validated within the context of the user’s particular environment (a service which TotalLab can provide in the form of IQOQ during installation), and to ensure that the compliance elements that sit outside of the software are implemented appropriately.
Download the Compliance Guide Here: